ZK/SEC Research notes from zkSecurity
All posts
announcement · tools · security

You like Circom but you find it confusing? Introducing Circomscribe

circomscribe

If you've been working in the field of zero-knowledge in the last few years you must have heard of Circom, a tool to write zero-knowledge applications in the form of circuits. Many projects have used Circom, that is the least one could say, as perhaps most ZK projects that have been built as smart contracts directly on Ethereum have been built using Circom; the most infamous project probably being TornadoCash.

While Circom has been great for developers wishing to explore usecases brought by zero-knowledge proofs, it is an extremely low-level tool, and it has proven to be quite hard to use correctly. One could almost say that if you don't understand how circuits (or proof systems) work at a low-level, you're going to run into trouble.
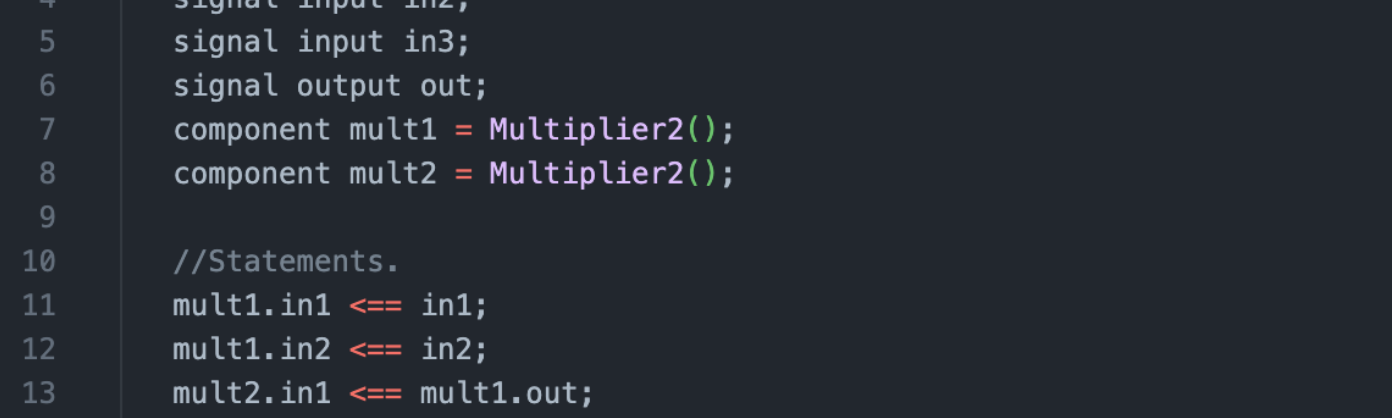
circom program example

As part of auditing ZK applications, zkSecurity has gone through its fair share of Circom circuits audits, and has realized that one of the biggest source of bugs (besides human error) is that developers have little idea of how their code eventually gets transcribed into "constraints" by the Circom compiler. In a way, it is similar to not being able to see the assembly your code compiles to, and as such making wrong assumptions sometimes.

While many more user-friendly and secure zk platforms and tools are making their way in (including our own in-house noname), the ecosystem of today is still very much based on Circom. So what can we do about this?

I say: let's improve everyone's understanding of how their Circom code gets compiled down to constraints! The more we educate developers, the less bugs they will write. To achieve this, we'd like to introduce Circomscribe.

Circomscribe is a tool that shows you what Circom does with your code. Simple as that. Paste your complete circuit in the tool, press a button, and quickly get an idea of what lines of code produce what constraints (if any).

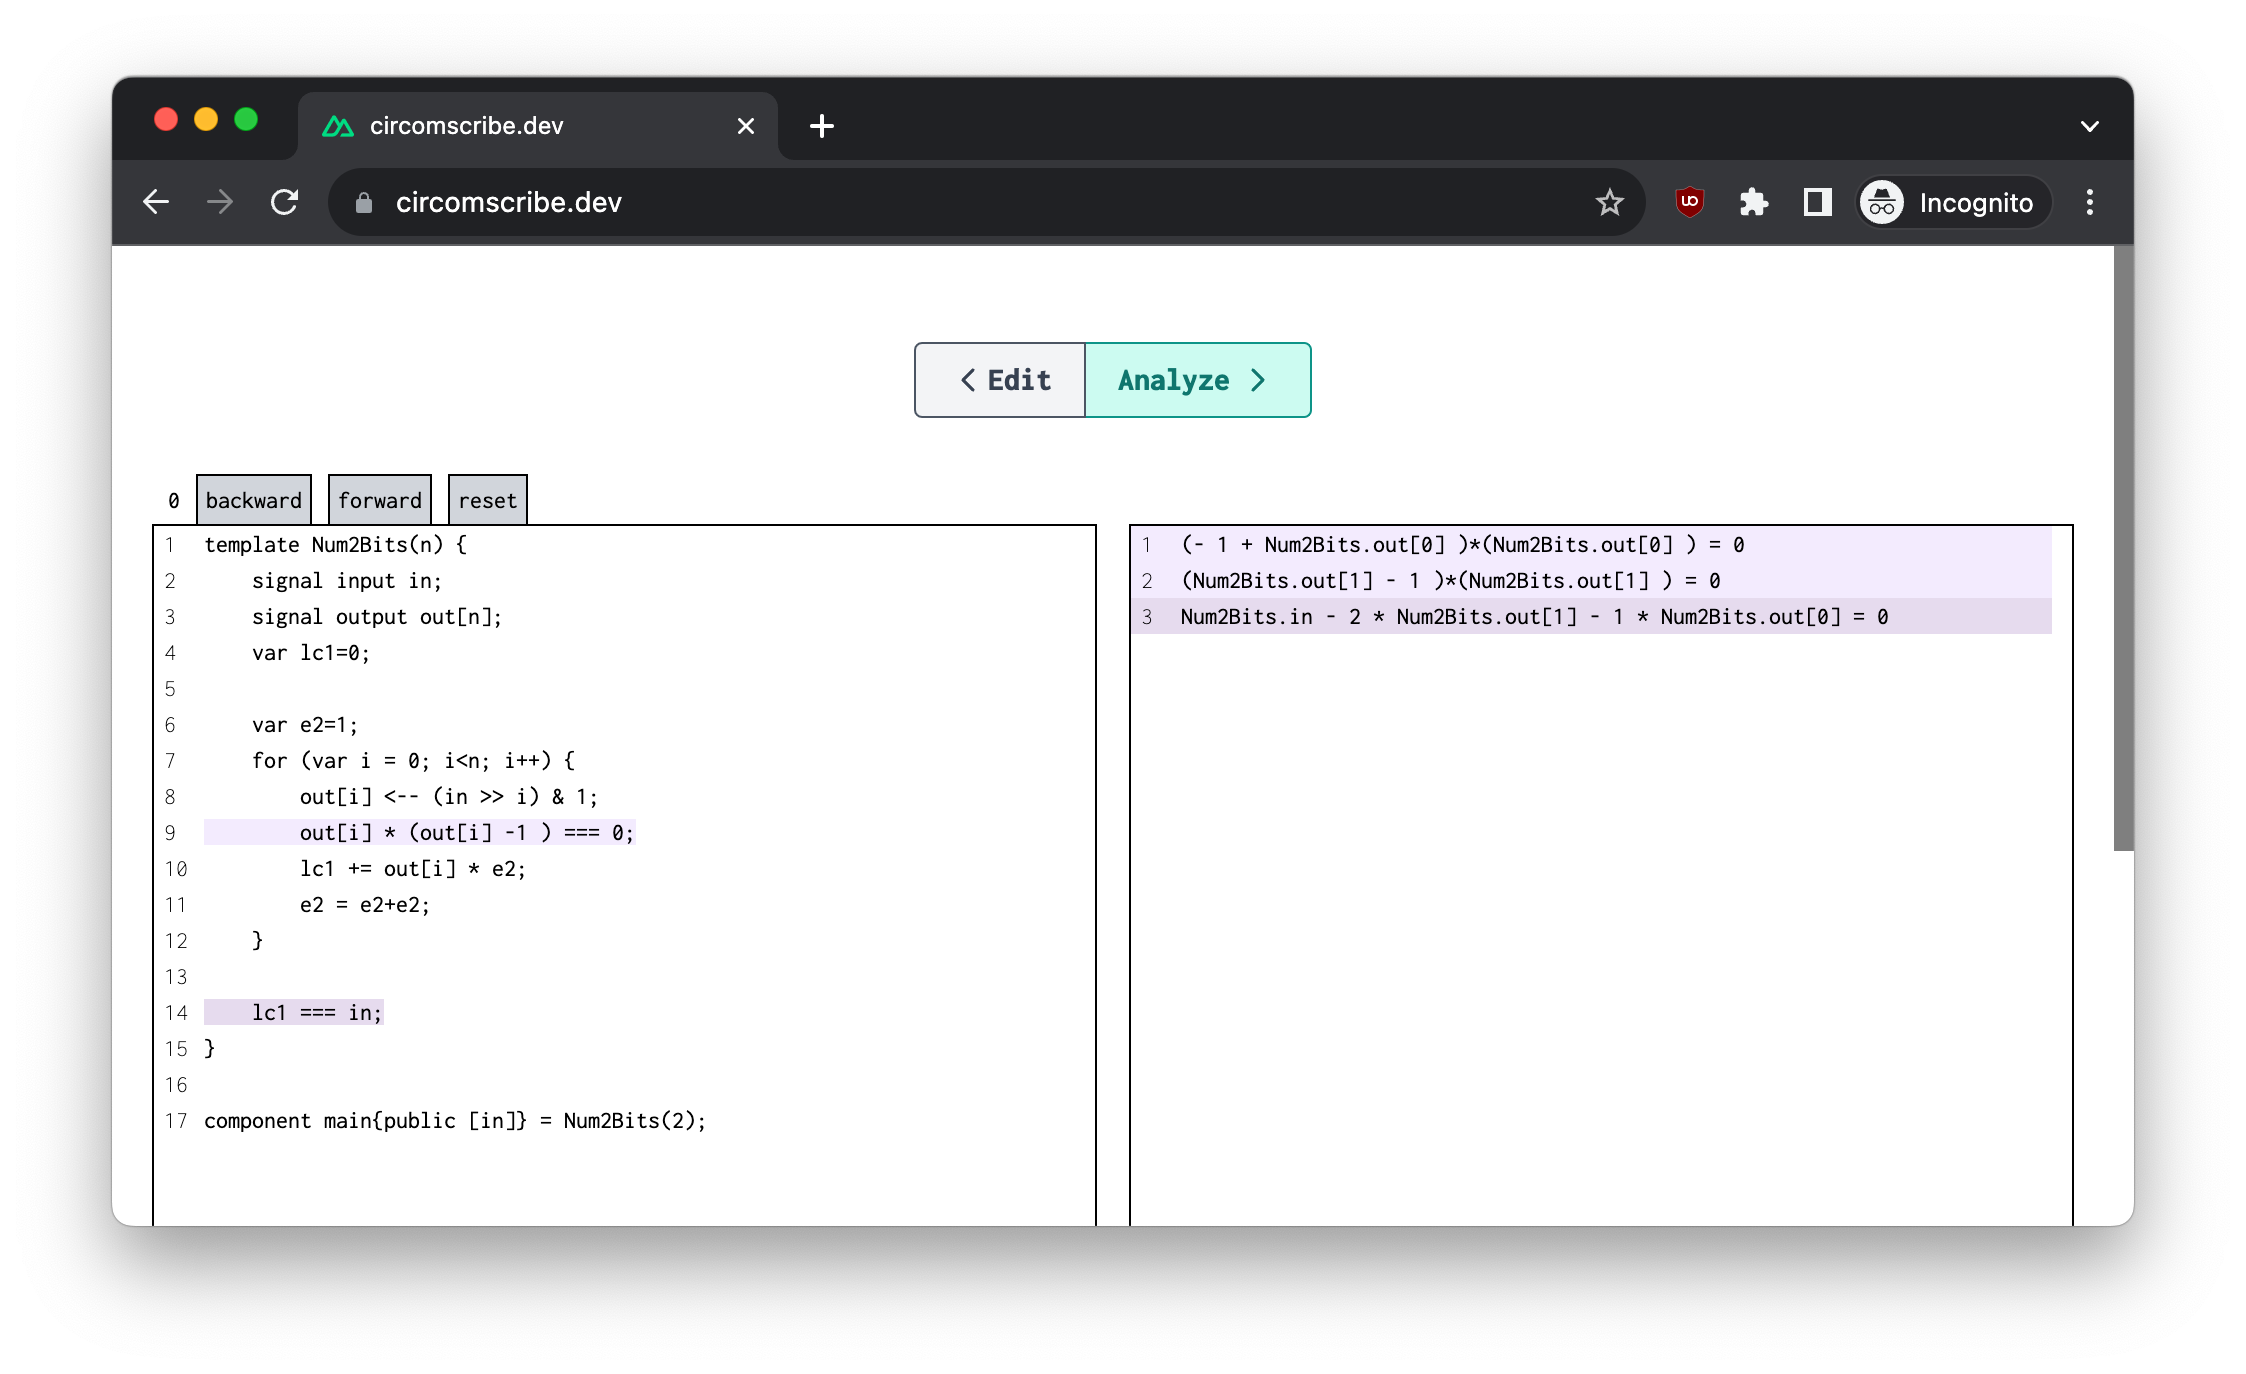
For example, here's the analysis of the Num2Bits template (which converts a value to a list of bits) taken directly from circomlib, the standard library of Circom:
Circomscribe

As you can see, only the lines of code that are highlighted on the left produce constraints. These constraints are "pure" constraints, which is what the compiler produces before actually unrolling the circuit (for example, if a template is used several times) and before any optimizations are performed. So in a sense, this is purely useful to understand the first pass of the compiler, but not useful to see what the actual compiled circuit looks like.

Underneath, Circomscribe is essentially a modified version of the Circom compiler to run in WASM and emit information in a JSON format when compiling. As of now, the Circomscribe tool provides simple features that we hope will be useful to developers and other security engineers. We hope to add more features in the future. If you have any ideas, please let us know!

Keep reading
Recommended

Common Circom Pitfalls and How to Dodge Them, Part 1

Programming in Circom comes with its fair share of challenges. After reviewing numerous Circom codebases, we’ve identified certain anti-patterns that occur frequently. In this series, we’ll provide a comprehensive overview of these issues to help you avoid the most common pitfalls. Of course, this won’t be a complete list of every mistake possible (Circom has plenty of ways to trip you up). But the footguns we’ll cover are the ones that tend to catch developers off guard the most.

Marco Besier · June 24, 2025

Introducing clean, a formal verification DSL for ZK circuits in Lean4

We're diving into our new project called **clean**, aimed at creating an embedded DSL and formal verification framework for Zero Knowledge (ZK) circuits using Lean4. Imagine being able to not only define ZK circuits but also formally prove their correctness. Sounds like a game-changer, right? We'll walk you through our process of building a robust library of reusable, verified circuit gadgets, focusing on the importance of soundness and completeness. Plus, you'll get a peek at some cool examples like 8-bit addition and how we're tackling ZKVM design with techniques borrowed from Fibonacci sequences. It's exciting stuff, and if you're curious about how we're paving the way for bug-free ZK circuits, this is a read you won't want to miss!

Giorgio Dell'Immagine · March 27, 2025

Public report of Darkfi circuits and crypto audit

In February 2024, we dived into a security audit of Darkfi's built-in contracts and circuits, putting them under the microscope to ensure everything checks out. Curious to know what we discovered while navigating the public Darkfi repository? Check out our full report for insights and findings.

ZK/SEC · February 27, 2024
More to explore

10 Must-Read Papers That Shaped Modern Zero-Knowledge Proofs

Zero-knowledge proofs have come a long way in 40 years, thanks to groundbreaking work from many brilliant minds. We're taking you on a tour of the key milestones in this fascinating journey, from the foundational concepts in 1985 by Goldwasser, Micali, and Rackoff, to modern applications and innovations like STARKs and zkVMs. You'll get a taste of major papers and projects that have pushed these proofs from theoretical curiosity to practical and scalable solutions. Dive into the history, understand the evolution, and see how these cryptographic marvels continue to shape the future of secure computation!

ZK/SEC · November 12, 2024

zk.golf: Fearless and Collaborative Optimization of Circuits

zk.golf is a platform where people can compete on creating the most efficient zk circuits for specific problems. It is enabled by what we call "fearless optimization", which is achieved by combining formal verification and frontier AI models. By the end, you will be convinced that nobody should look at constraints ever again in their life.

Giorgio Dell'Immagine, Mathias Hall-Andersen · July 02, 2026

A Year of ZK Security

A year after launching, we've grown and evolved alongside the world of zero-knowledge proofs, uncovering bugs and learning the ins and outs of ZK technology. From circuit audits to developing our own tools like Circomscribe, it’s been a wild ride. We've discovered how easy it is to misstep with ZK code, especially as these systems grow complex and impact financial security. As zkVMs gain popularity, we're excited about the challenges ahead and are expanding our expertise. Want to dive into the world of ZK with us? Check out our latest projects and even take on our zkBank challenge!

David Wong · May 30, 2024