ZK/SEC Research notes from zkSecurity
All posts
educative · zk · sumcheck

Learn Sumcheck, MLE, and HyperPlonk: An Interactive Tutorial with SageMath

We've released a new interactive tutorial on Sumcheck, Multilinear Extensions (MLE), and HyperPlonk that focuses on implementation rather than just theory. The course includes complete SageMath code and exercises so you can actually build these protocols yourself.
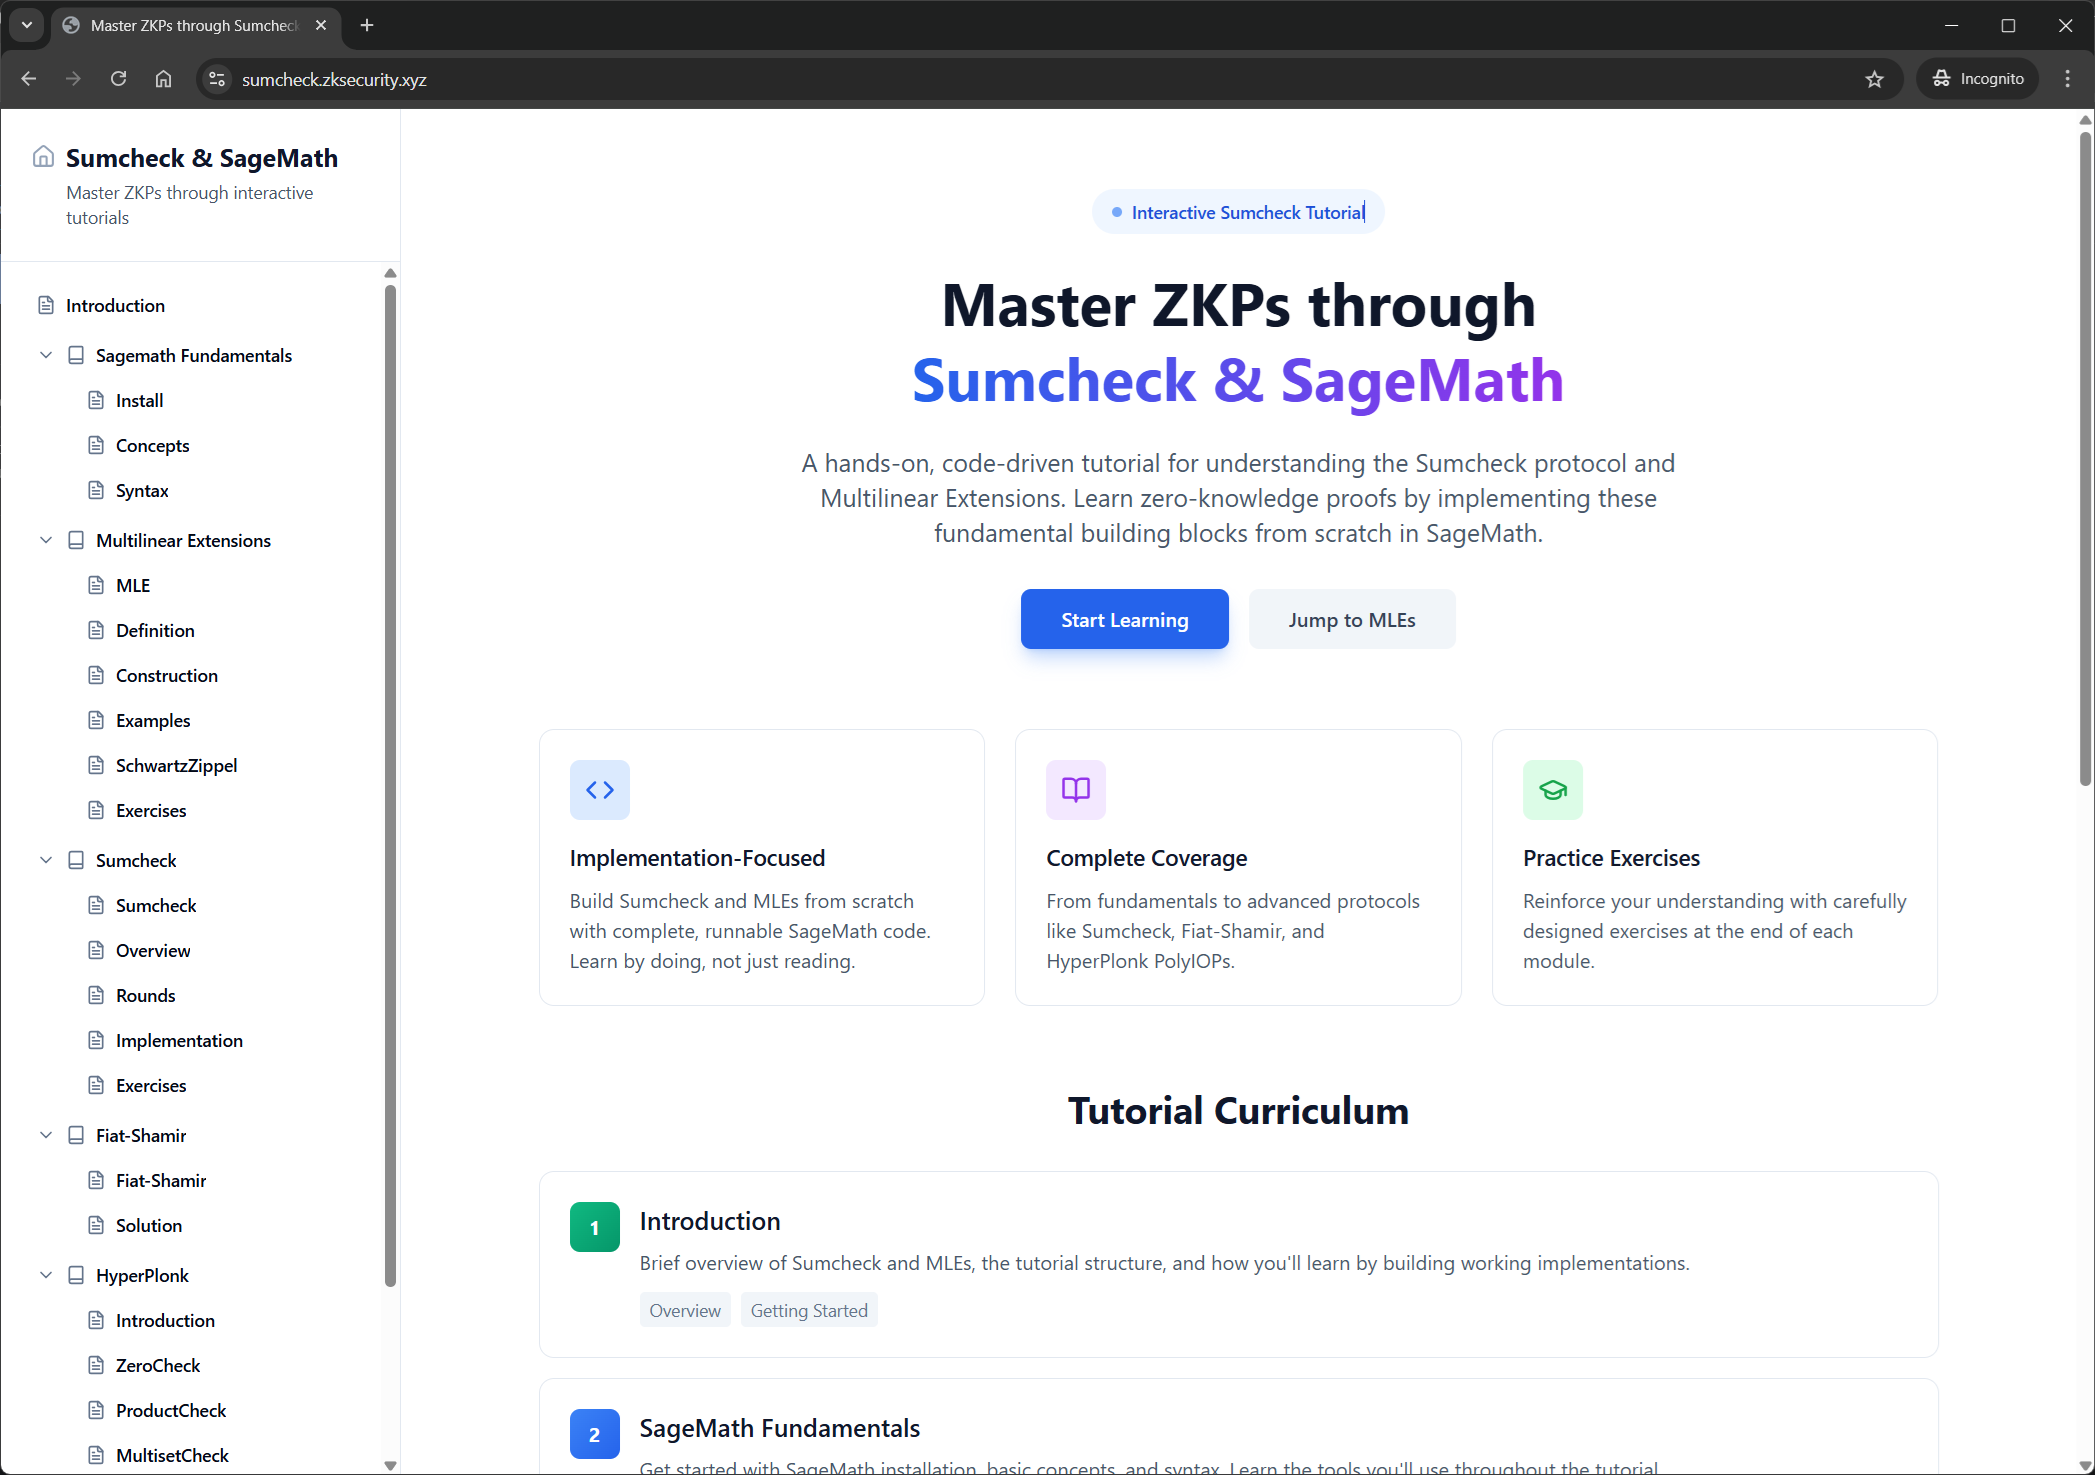
webpage

The Sumcheck protocol shows up everywhere in modern zero-knowledge proofs scheme such as HyperPlonk, Spartan, Jolt, and more all. But understanding the papers is one thing; implementing the protocols is another. This tutorial bridges that gap by walking you through working implementations in SageMath, starting with the basics of multilinear polynomials and building up to a complete proof systems.

Hands-On Learning

The tutorial comes with runnable code examples for every protocol. You'll work through interactive exercises implementing key parts of the protocols yourself: evaluating multilinear polynomials, building the prover and verifier algorithms, and composing multiple Sumcheck instances together.

SageMath makes it easy to experiment with the math directly without getting bogged down in performance optimizations. You can focus on understanding how the protocols actually work, which polynomials get evaluated where, and why the verification works. Once you understand the math, porting to production languages becomes much easier.

The course assumes no prior cryptography or sagemath knowledge. We start from first principles and build up progressively, so whether you're implementing zero-knowledge circuits or researching new protocols, you can follow along.

Get started at sumcheck.zksecurity.xyz.

Keep reading
Recommended

Faster Sumchecks: Part I

In this blog post, we explore how to optimize the sumcheck protocol, particularly when working with values in a small field and randomness from a large field, as often needed in zkVMs. We introduce various algorithms aimed at reducing expensive operations, focusing on minimizing large multiplications. Starting from using simple evaluation tables to more sophisticated techniques like precomputing accumulators and leveraging Lagrange interpolation, we demonstrate how to efficiently organize computations to speed up proving times. Readers will gain insights into handling arithmetic operations within the sumcheck protocol and learn about optimizing specific cases in zero-knowledge proofs.

Jason Park · November 21, 2025

Sum-Check as an Algebraic Tensor Reduction: Part I

This post introduces algebraic tensor reductions as a unifying framework for understanding recursive proof protocols, using sum-check as the main motivating example. It walks through one recursive step of sum-check, showing how the prover sends a univariate summary, the verifier checks sum consistency, and the original claim is reduced to a smaller claim with one fewer variable. A small bivariate example illustrates how this “peel off one variable, check, then fold with randomness” pattern works concretely. The post sets up the rest of the series, which will introduce the tensor language needed to recover classical sum-check as an algebraic tensor reduction.

Marco Besier · April 27, 2026

𝒫𝔩𝔬𝔫𝒦: A Hands-On Deep Dive

𝒫𝔩𝔬𝔫𝒦’s many layers (selector polynomials, wiring permutations, quotient tests, random challenges and KZG commitments) can be overwhelming. Our zkSecurity tutorial uses a single running example to demystify them all. Build tables and interpolate low-degree BN254 polynomials, encode gate and wiring constraints, run deterministic and probabilistic zero-tests, then layer in randomness and KZG commitments to produce a full Fiat–Shamir proof. Grab the Jupyter Notebook (Sage or Cocalc), or work in your favorite language with our guided test cases.

Martín Ochoa · August 05, 2025
More to explore

zkBitcoin: Use Zero-Knowledge Applications (zkapps) on Bitcoin

We're excited to introduce zkBitcoin, a new tool that lets you create zero-knowledge applications on Bitcoin using a minimal layer 2 protocol. This innovation opens up a world of complex, privacy-focused apps by enhancing Bitcoin's scripting capabilities. We're currently on testnet, so you can jump in and explore the possibilities. Check out our whitepaper or watch some videos for a deeper dive. It's an exciting time for Bitcoin development, and we can't wait to see what you'll build!

David Wong · January 31, 2024

Public report of Lighter ZK circuits

We recently teamed up with Lighter to dive deep into their custom ZK circuits used for a verifiable orderbook matching on a Layer 2 exchange. Our findings show solid and well-structured code, thanks to their cooperative engineering team. The post gives a fascinating look into how Lighter’s ZK rollup ensures valid state transitions on Layer 1 through zero-knowledge proofs and the innovative structure of their order book matching process. It explains the roles of the main operation and exit hatch circuits, while also touching on how users can exit in emergencies. It's a great read if you're curious about how these systems maintain security and efficiency in decentralized finance.

ZK/SEC · April 24, 2024

Notes and Proofs for Divisor Techniques

Notes and proofs for the divisor-based ECIP protocol of Eagen, written with Diego F. Aranha and supported by MAGIC Grants. The document is self-contained: it works through the necessary algebraic geometry, the interactive proof and its soundness, the composition with a simulation-extractable NIZK, and the R1CS verifier circuit used by Parker's gadget in Monero's FCMP++.

Mathias Hall-Andersen · May 08, 2026