ZK/SEC Research notes from zkSecurity
All posts
noname · Part 1 of 4

noname: ZK app developers should be able to see down to the constraints

noname

As we've explained before, zero-knowledge apps (or ZK apps) will come in two different shapes: VM instructions and arithmetic circuits.

VM instructions should sound familiar. Reading them is like reading assembly, and they're a level of abstraction higher than arithmetic circuits (as pointed out by this post).

Whatever they're writing, real programmers need to see what their programs compile down to (according to John Carmack). That's how you find unoptimized bits as a low-level code monkey, but it's also how you find some security issues and bugs. It's not just that compilers have bugs, it's also that ZK developers are facing a new kind of programming. That is, when they'll be writing circuits (the VM-side of the ZK coin is not so new after all).

When writing zkApps, or ZK programs, that compile down to circuits, developers will be faced with a restricted and unsafe environment. Restricted because they will have to optimize their code to fit into the circuit size limits, and unsafe because they will need to ensure that what needs to be constrained is correctly constrained (we'll be writing more on that!).

Low-level developers know exactly what this means: they need access to the machine-generated code, the "assembly", the lowest possible layer. They need the source of truth.

For zkApps in proof systems like PlonK, that source of truth is the list of gates, and the wires, that describe the circuit. This list of gates and the wiring is often obtained by compiling a program written in a higher-level language or framework.

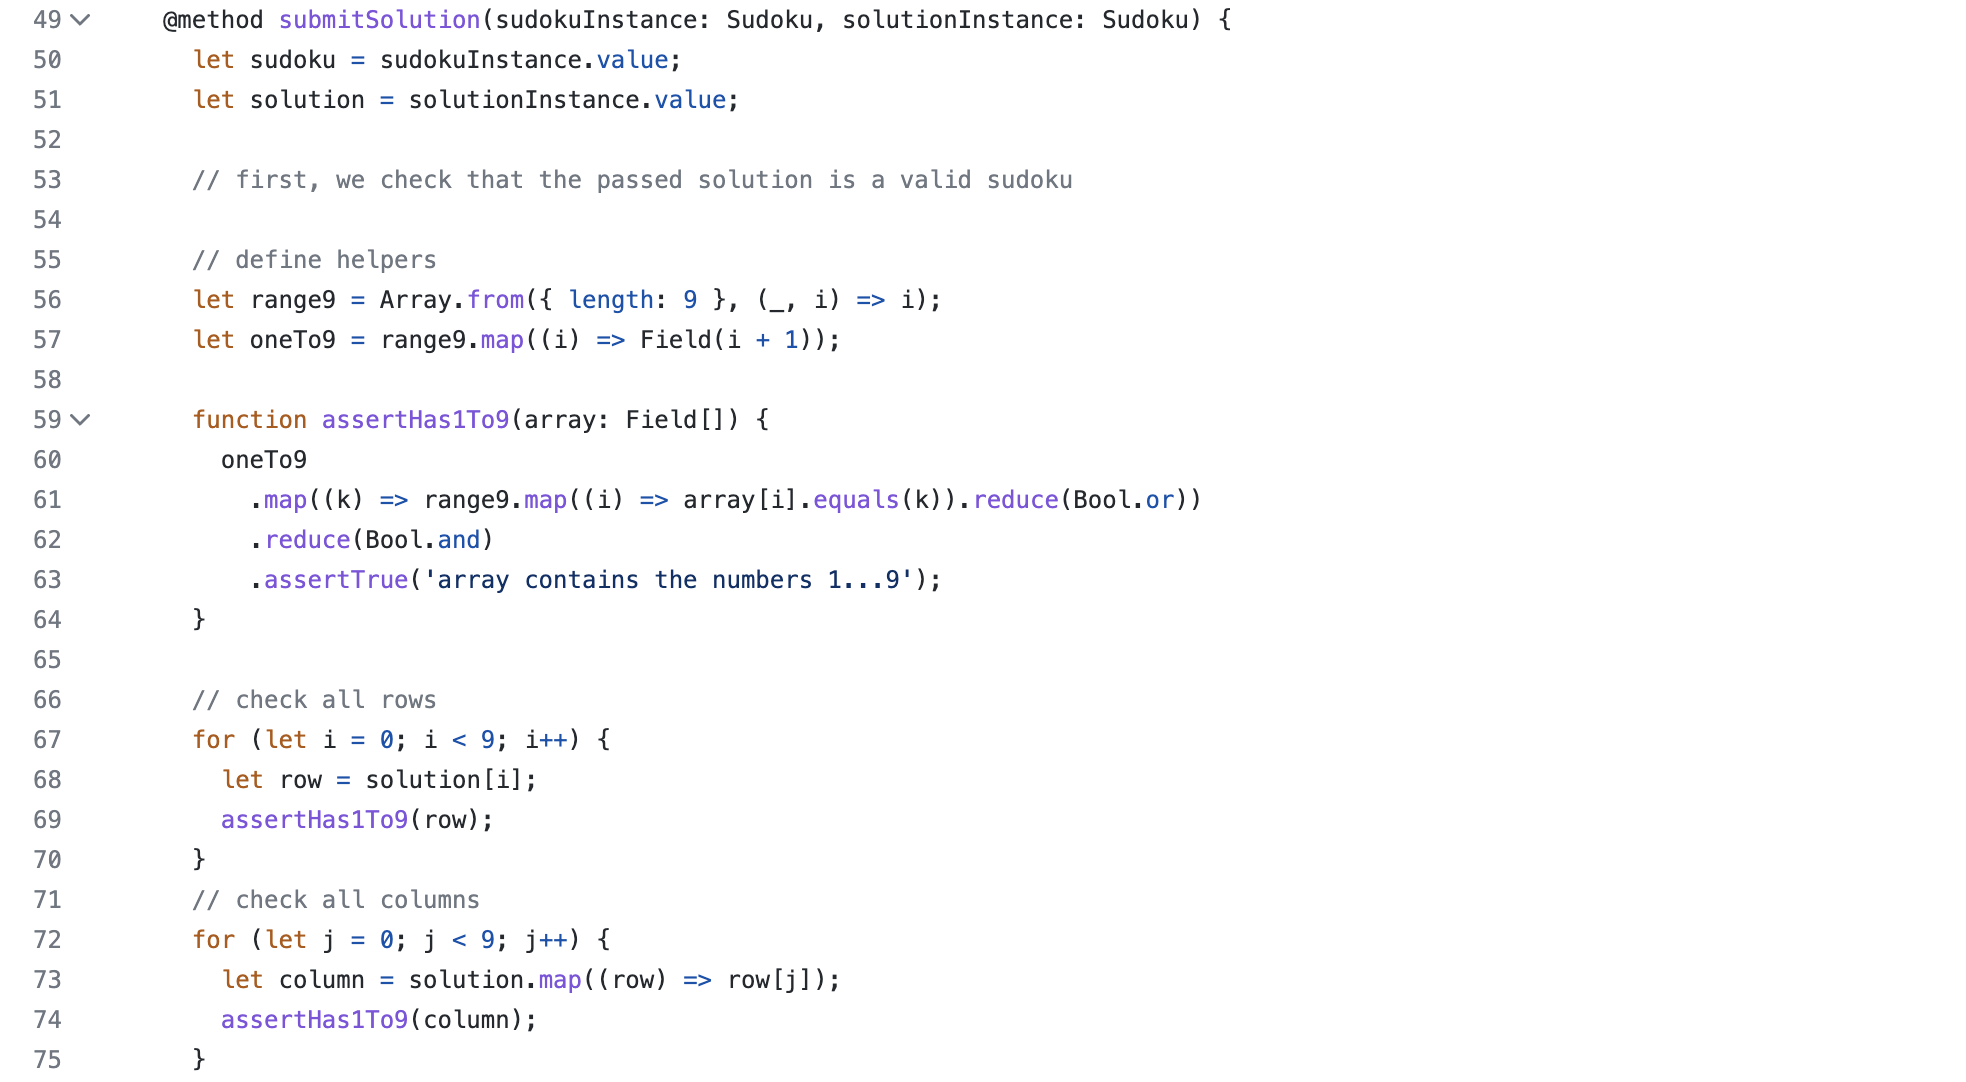
SnarkyJS is one example of a framework that helps developers write circuits in typescript without having to think about or understand circuits, or having to learn a new language.
snarkyjs

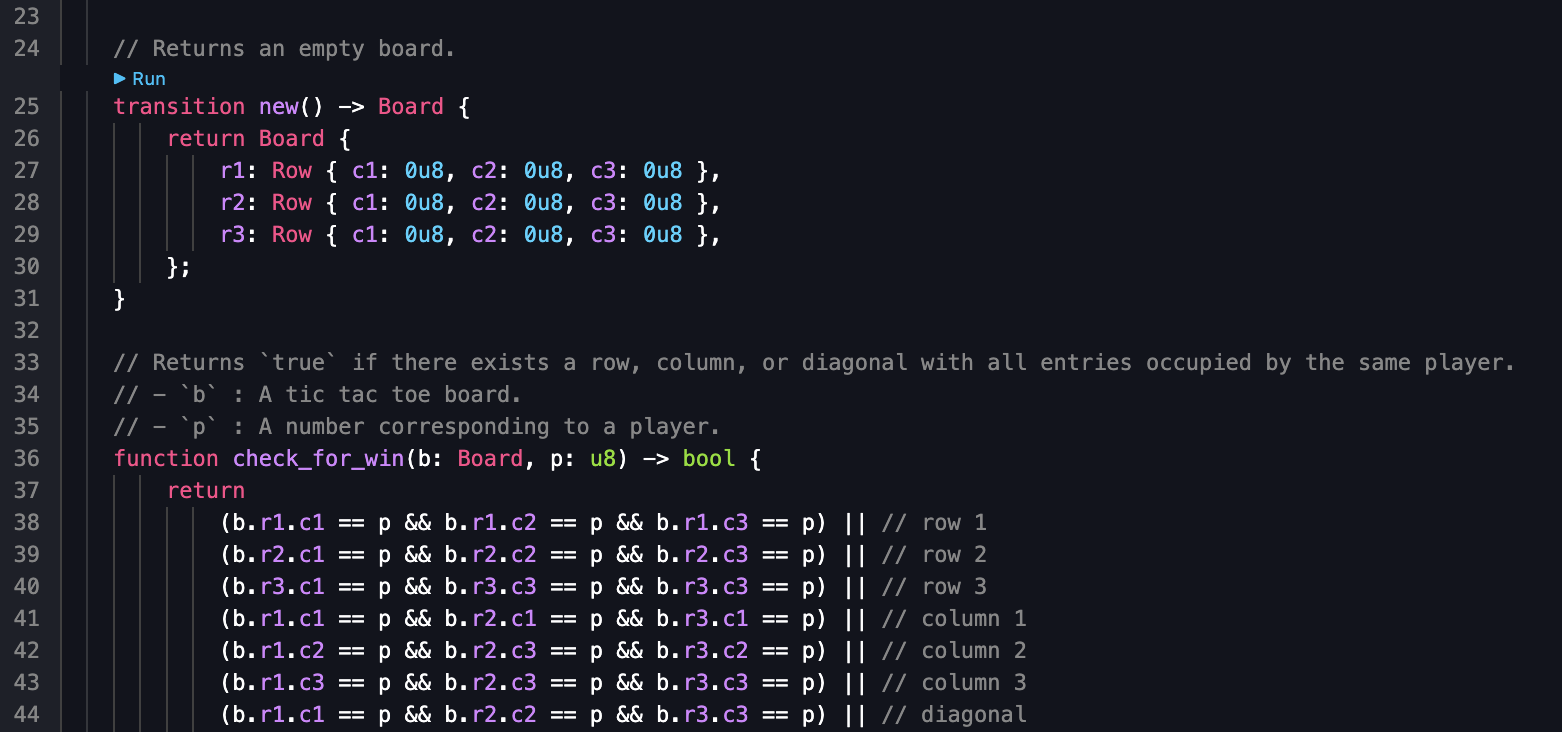
As you can see, it mostly looks like typescript decorators and library function calls. On the other hand, Leo is one example of a made-up programming language that offers the same thing.
leo

Both of these approaches offer different benefits and downsides. The framework approach can rely on the preexisting tooling of the language the framework is written in. On the other hand the DSL approach prevents developers from making some types of mistakes by mixing in logic that does not get constrained (but that's not always true depending on the DSL, as Circom has shown us).

What the children of both approaches all seem to be lacking though, is a way to see the "assembly" a program compiles down to.

Better toolings need to become available.

At zksecurity.xyz, we've experimented with a new programming language called noname (initially meant as a placeholder name). noname allows developers to write zkApps in a high-level language that looks like a mix of Golang and Rust:

use std::crypto;

fn main(pub public_input: Field, private_input: [Field; 2]) {
    // checks that they add up to 2
    let res = private_input[0] + private_input[1];
    assert_eq(res, 2);

    // checks that one is the hash of the other
    let digest = crypto::poseidon(private_input);
    assert_eq(digest[0], public_input);
}

The particularity of noname is that you get extensive debug information on how such programs compile down to gates. For example, passing the --debug argument to noname gets you an output describing the "assembly". A list of gates, where each gate is accompanied with an explanation as to why it exists and what line of code it comes from.
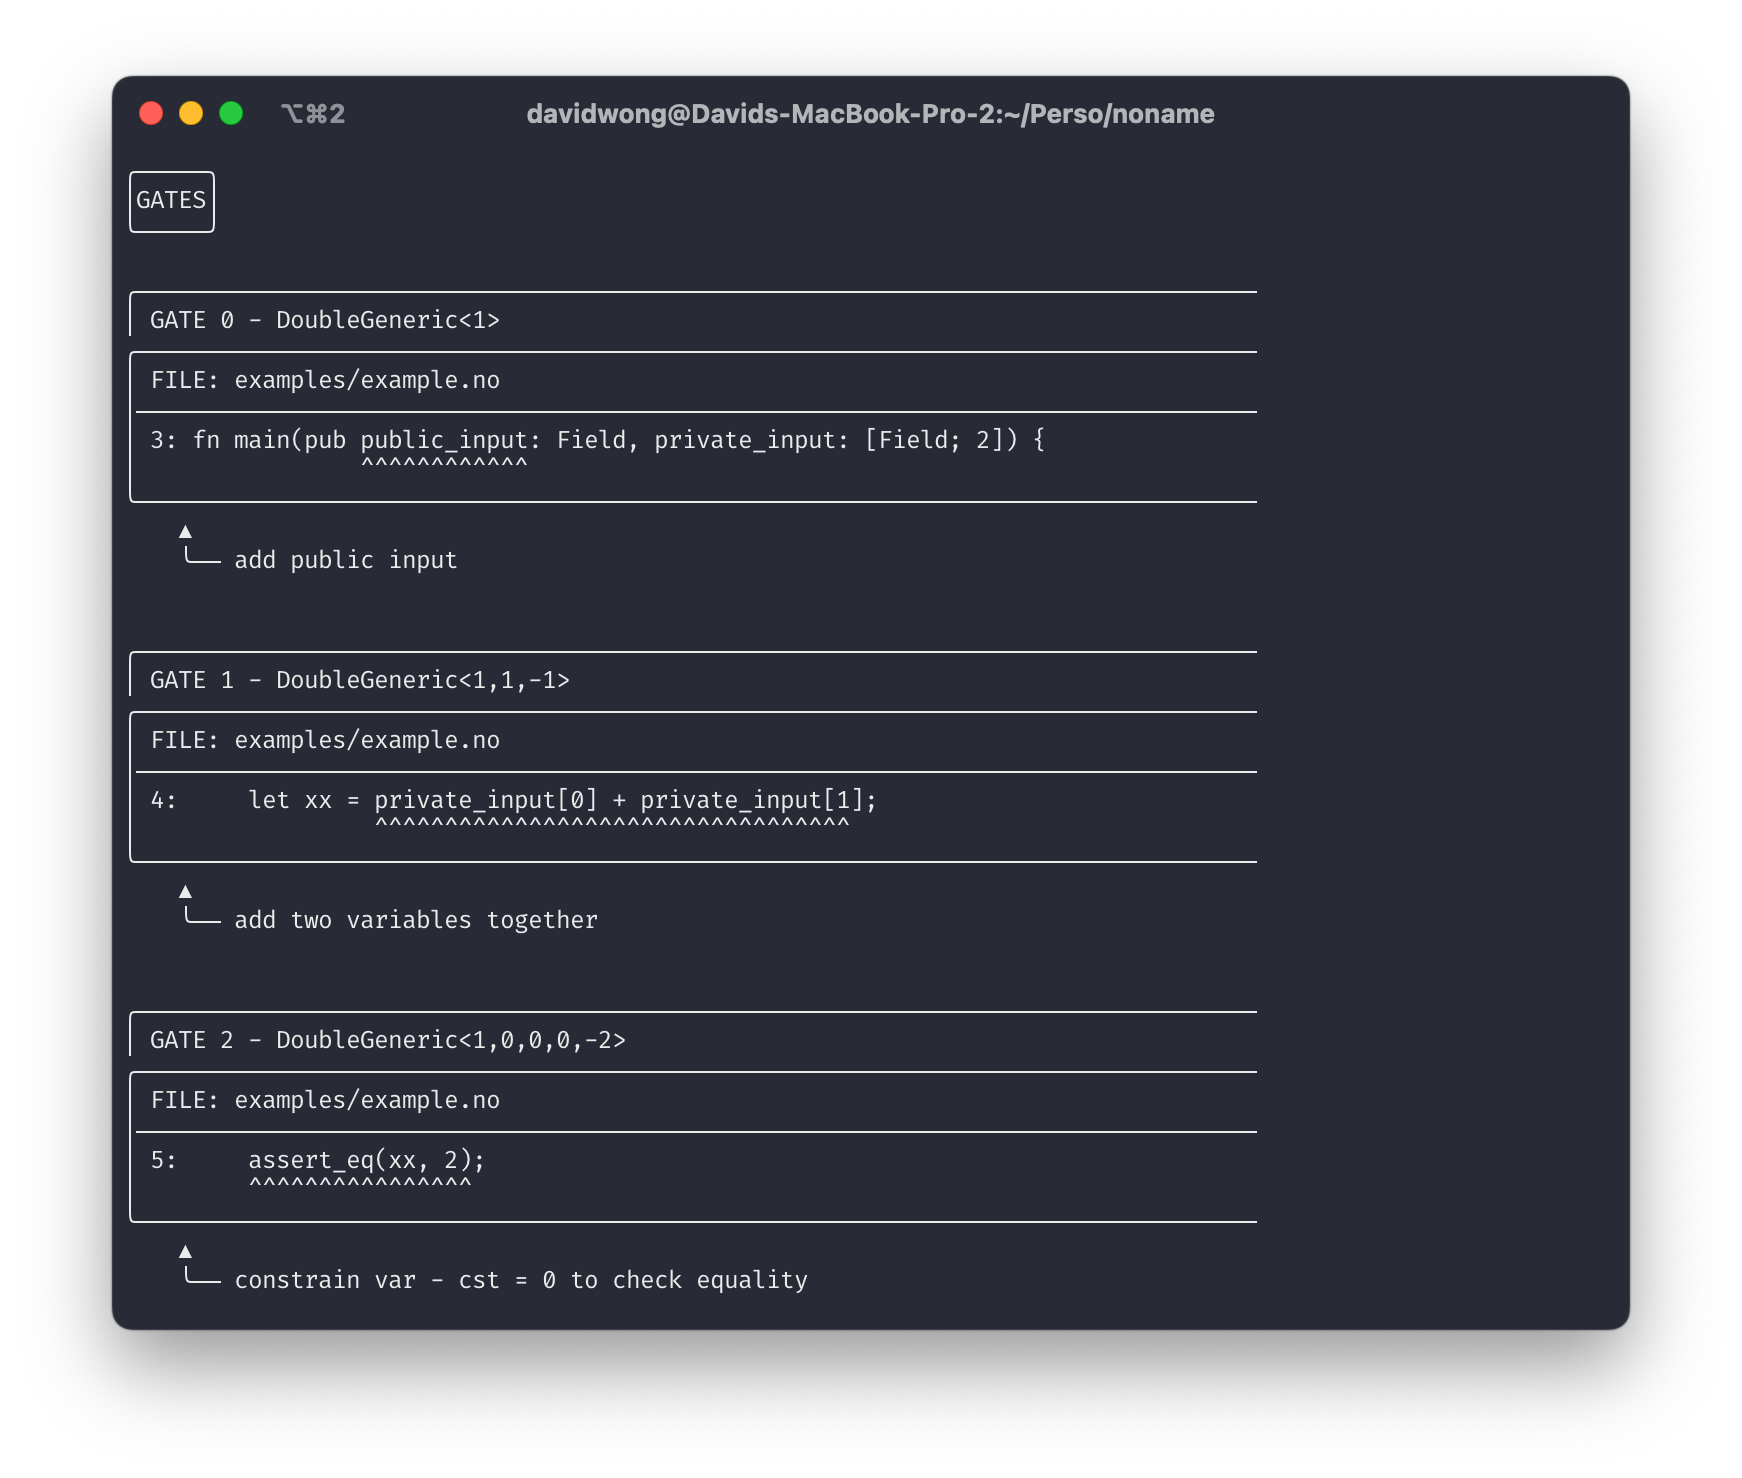
In addition, the wiring is also displayed at the end with similar information about the source of their existence:
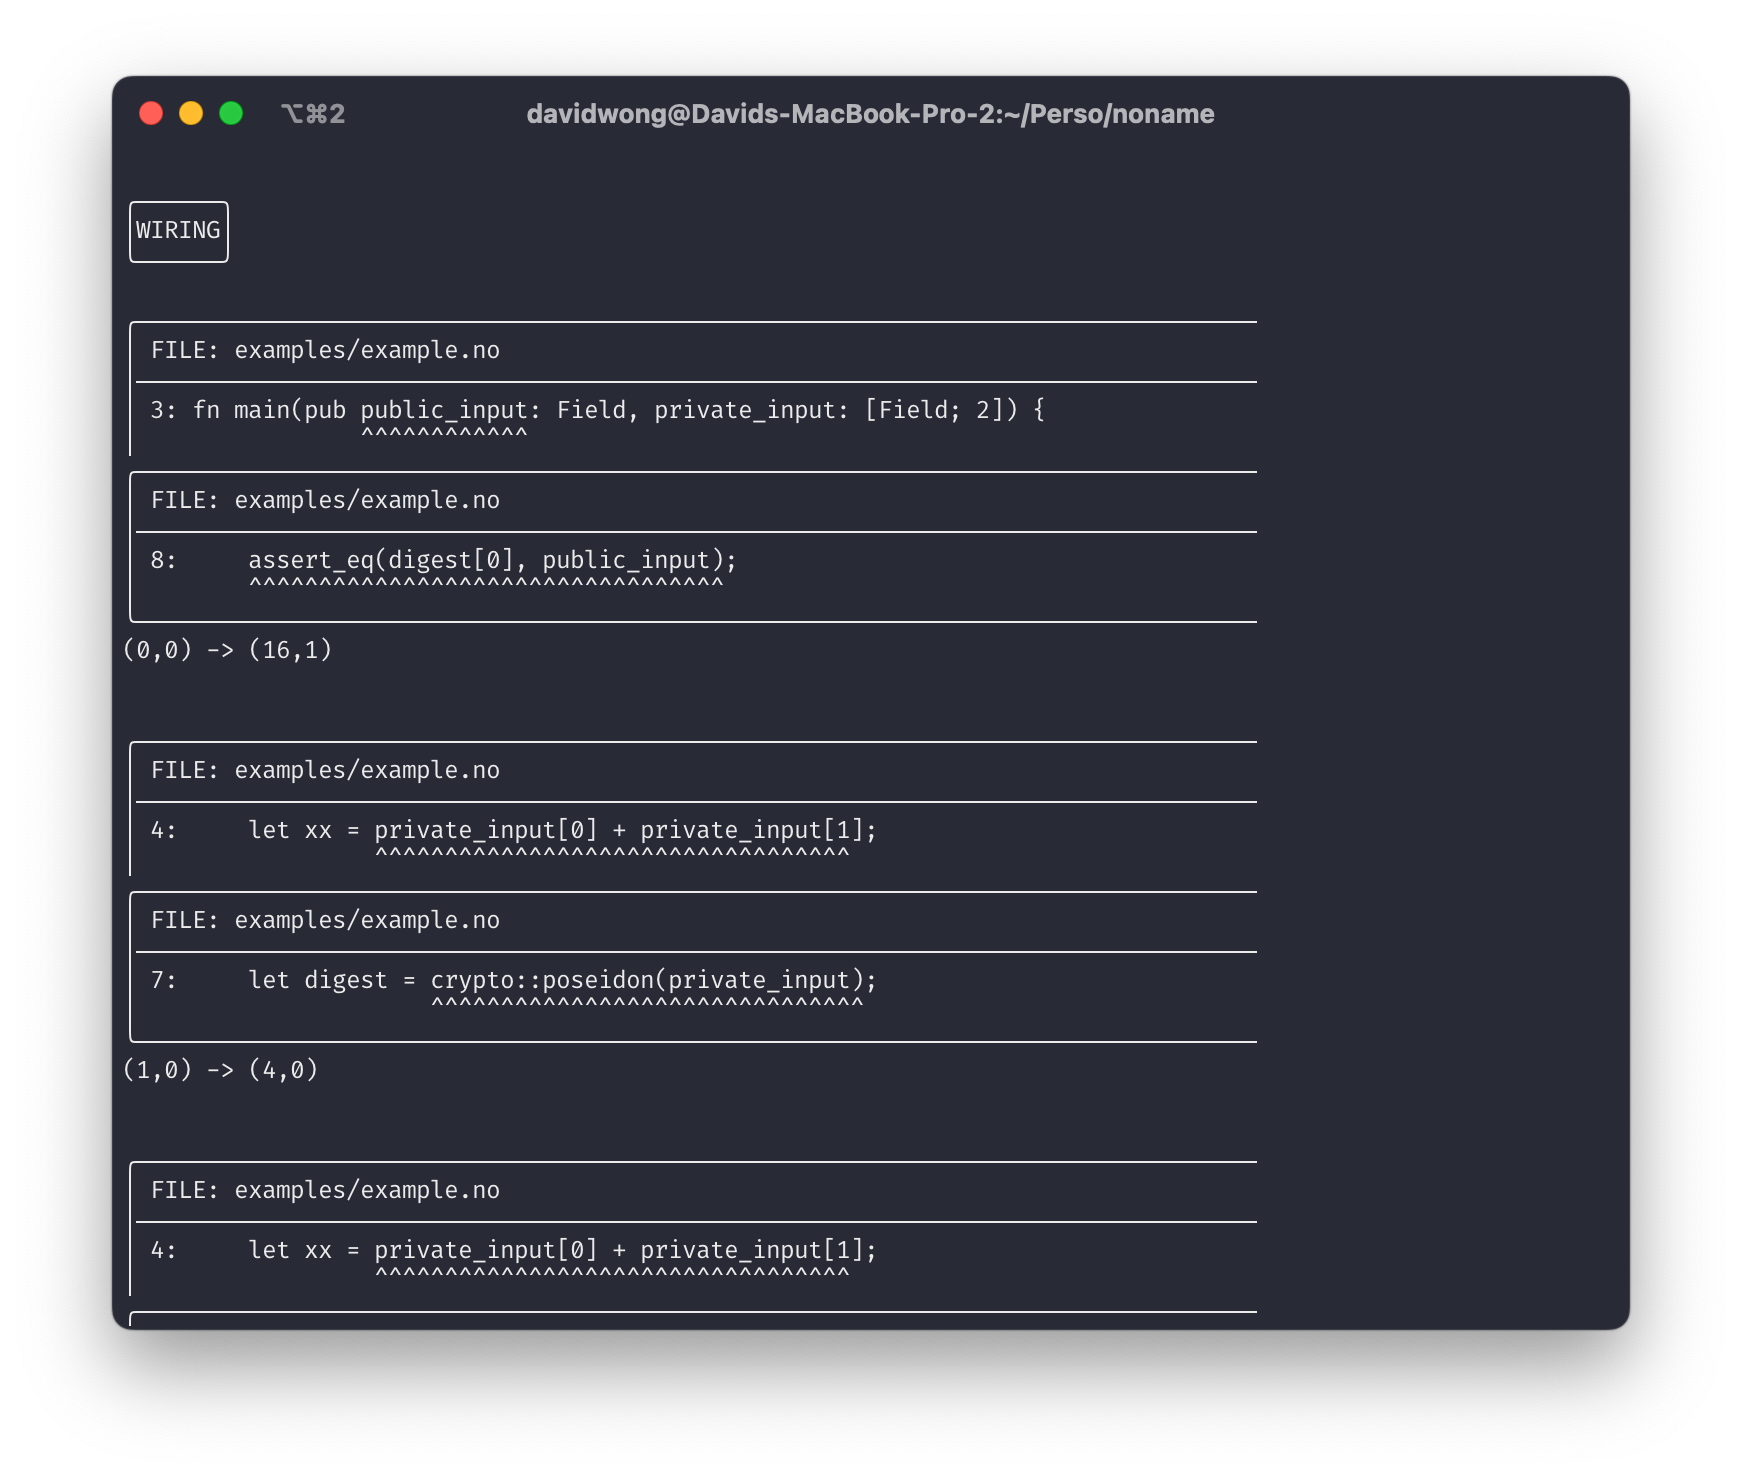
noname, at the moment, is more of a toy language that we've used to understand other compilers, and the type of compiler bugs that can occur. We've also used it to teach how to read ZK circuits!

While the project is still experimental, we're excited to see if this will inspire more people to build better debugging tools, as well as lead to students (in school or at heart) using noname to learn about how arithmetic circuits are constructed.

Head over to our repo to try it out!

Keep reading
Recommended

noname 2.0: Unlocking Numeric Generics, Folding Schemes, and a Playground

We're excited to introduce the preview of noname 2.0, packed with features that make developing advanced ZK circuits easier than ever. This update includes flexible generic-sized arrays, seamless integration with folding schemes for IVC, and an interactive online playground to test and share code. We've also optimized R1CS constraint generation to boost performance. Plus, there are numerous community-driven enhancements and bug fixes that make the language more robust and user-friendly. Dive in to explore the specifics of our journey, learn from the contributions of our vibrant open-source community, and see how noname is evolving into a more versatile tool for developers.

ZK/SEC · August 08, 2024

noname 3.0: Native Hints, Standard Library, Compiler Visualizer, And More!

We're super excited to introduce noname 3.0, our zk programming language inspired by Rust and Golang, now achieving full feature parity with Circom. This update brings native hints, a standard library, debugging features, and a lot more to enhance developer experience. Dive into how hint functions work with an 'unsafe' keyword to balance innovation and security, explore our new stdlib modules, and see how the compiler pipeline visualizer can help you understand the compiling process. Plus, check out our next steps and how you can contribute to shaping noname's future.

ZK/SEC · November 13, 2024

noname meets Ethereum: Integration with SnarkJS

We're excited to share that our programming language, noname, now supports R1CS, making it easier to write zero-knowledge (ZK) circuits and deploy them on Ethereum using SnarkJS. This update introduces an alternative to the common Circom language, with a simple and intuitive syntax inspired by Rust and Golang. In this post, we illustrate how to deploy a noname-based Sudoku circuit on Ethereum, demonstrating core benefits like proving a solution's correctness without revealing it. Dive in to explore how noname could potentially unify the fragmented zkSNARK ecosystem and simplify your circuit writing process!

Katat Choi · June 01, 2024
More to explore

Circle STARKs: Part III, Circle FFT

In this blog post, we explore how to efficiently implement polynomial operations using Circle FFT in the context of STARKs, drawing parallels with the Cooley-Tukey FFT. We discuss how the Circle FFT handles bivariate polynomials over the circle group, replacing traditional multiplicative subgroups with twin-cosets. You'll discover the nuanced process of decomposing and recomposing polynomials using projection and squaring maps, leading to efficient computations. We also address the gap between the polynomial degree space and the space spanned by Circle FFT. This is a fascinating dive into the heart of polynomial computations in cryptography.

Varun Thakore · August 04, 2025

Public report of Reclaim protocol's ChaCha20 circuit

We audited Reclaim protocol's ChaCha20 circuits, diving deep into bit-level operations for a secure and efficient design. After a few iterations, we switched from a word-based to a bit-focused circuit approach, achieving a 10% enhancement in performance and size. We used Circom for implementation, with a focus on Groth16 system constraints. Our findings led Reclaim to revamp their strategy, honing in on bitwise logic for an effective flow without costly re-encodings. Curious about the technical journey and the final audit insights? We’ve got the details covered!

ZK/SEC · October 02, 2023

Sum-Check as an Algebraic Tensor Reduction: Part II

In this part of our series, we start introducing the algebraic language needed to formalize sum-check as a tensor reduction. We start with the basics of rings and modules. Rings generalize fields by dropping the requirement that every non-zero element has a multiplicative inverse. Modules then generalize vector spaces by allowing scalars to come from a ring instead of a field. In this post, we’ll use plenty of examples to make these ideas concrete and build intuition along the way.

Marco Besier · May 10, 2026